Secure and comply
 TigerGate
Secure Every Application, From Code to Cloud
TigerGate unifies application security posture management, DevSecOps automation, and eBPF-powered runtime protection, so security and engineering teams can find, prioritize, and fix what actually matters before attackers do.
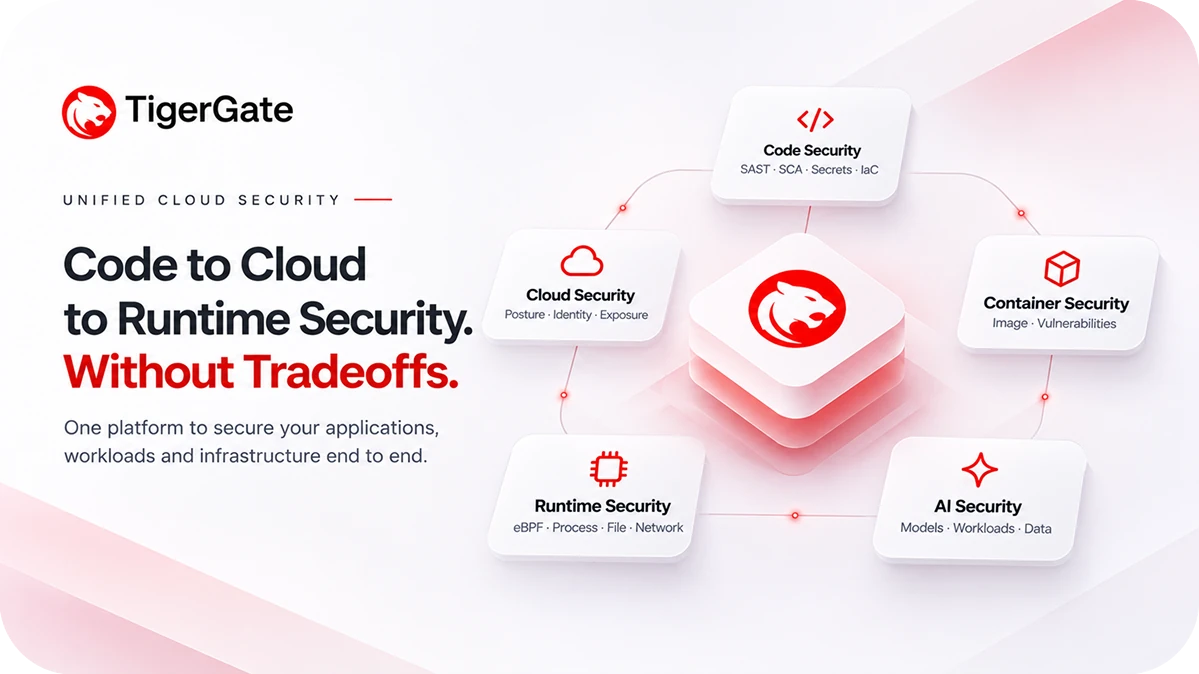
The Features Behind Every Secure Deployment

Complete Application Mapping
Automatically discover every repository, container, and cloud resource, then map how they connect so you always know your real attack surface.

Risk-Based Prioritization
Combine exploitability, internet exposure, and runtime reachability to surface the small fraction of findings that pose genuine risk.

Automated Remediation
Turn findings into pull requests with fix guidance, routed to the right code owners automatically, so issues get fixed instead of filed.

Shift-Left Scanning
Catch vulnerable dependencies, exposed secrets, and insecure IaC in the IDE and on every pull request, before code ever ships.

Kernel-Level Runtime Detection
Watch process execution, file integrity, and network activity in production with eBPF, tamper-proof visibility traditional agents can't match.

Compliance That Runs Itself
Map pipeline scans and runtime evidence straight to SOC 2, ISO 27001, and PCI-DSS controls for audit-ready reporting year-round.
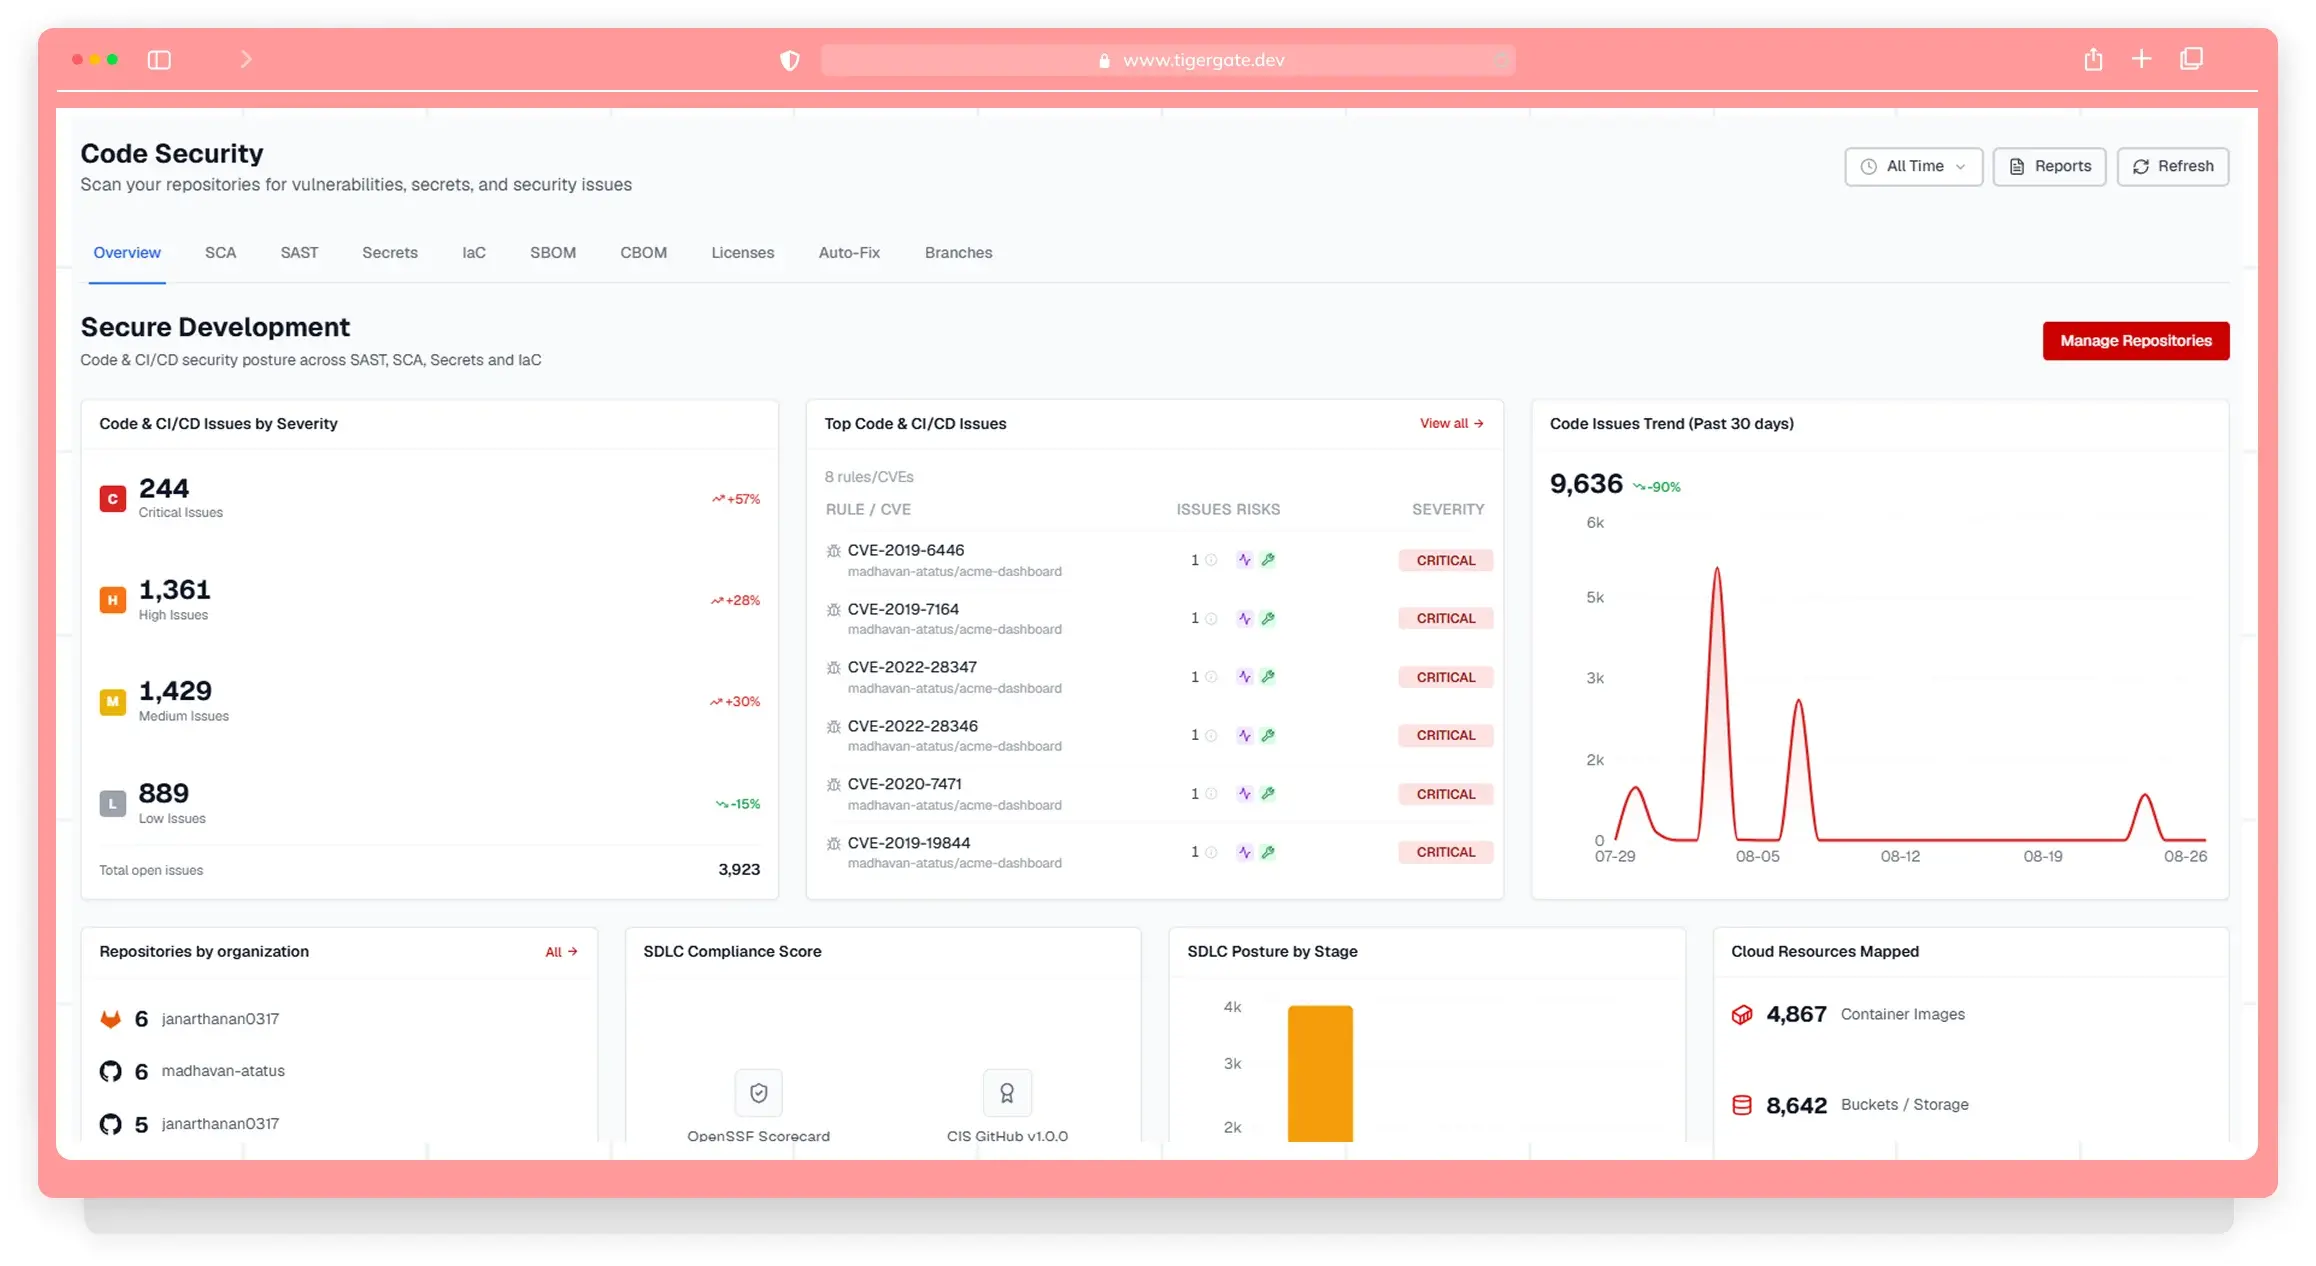
Complete Visibility Across Your Application Stack
Map your entire application attack surface from code to cloud. TigerGate consolidates findings from SAST, SCA, secrets scanning, and IaC analysis into a single, prioritized view, then filters out noise by checking what's actually reachable in production.
Try TigerGate free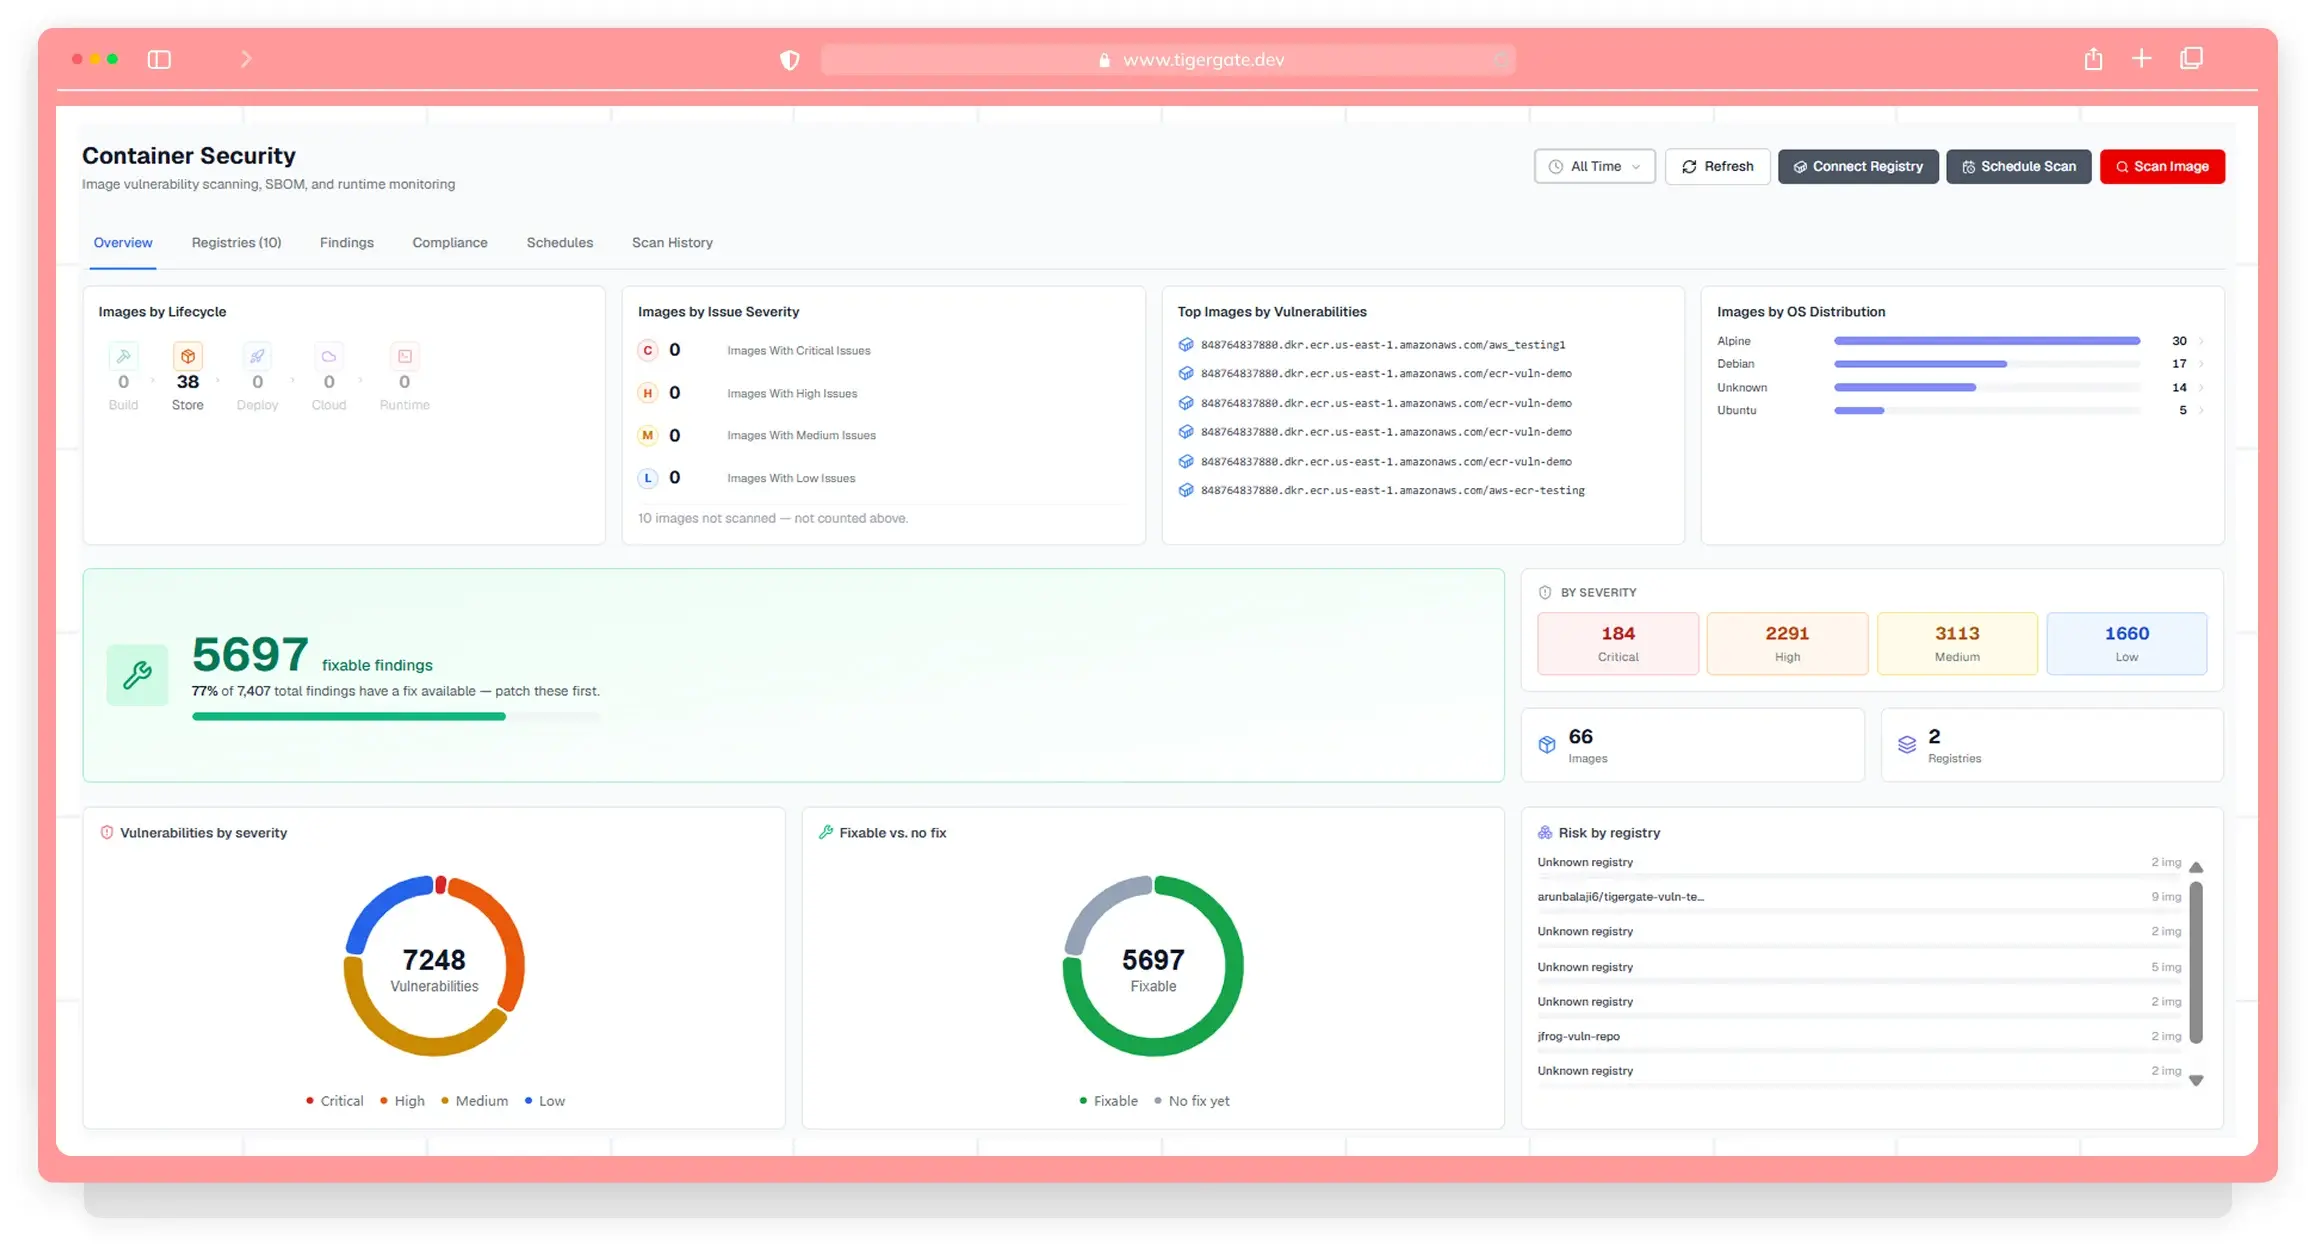
Security at DevOps Speed
Build security into every stage of the SDLC without slowing engineering teams down. TigerGate scans pull requests, container images, and infrastructure-as-code automatically, integrating natively with GitHub Actions, GitLab CI, Jenkins, CircleCI, and Azure DevOps.
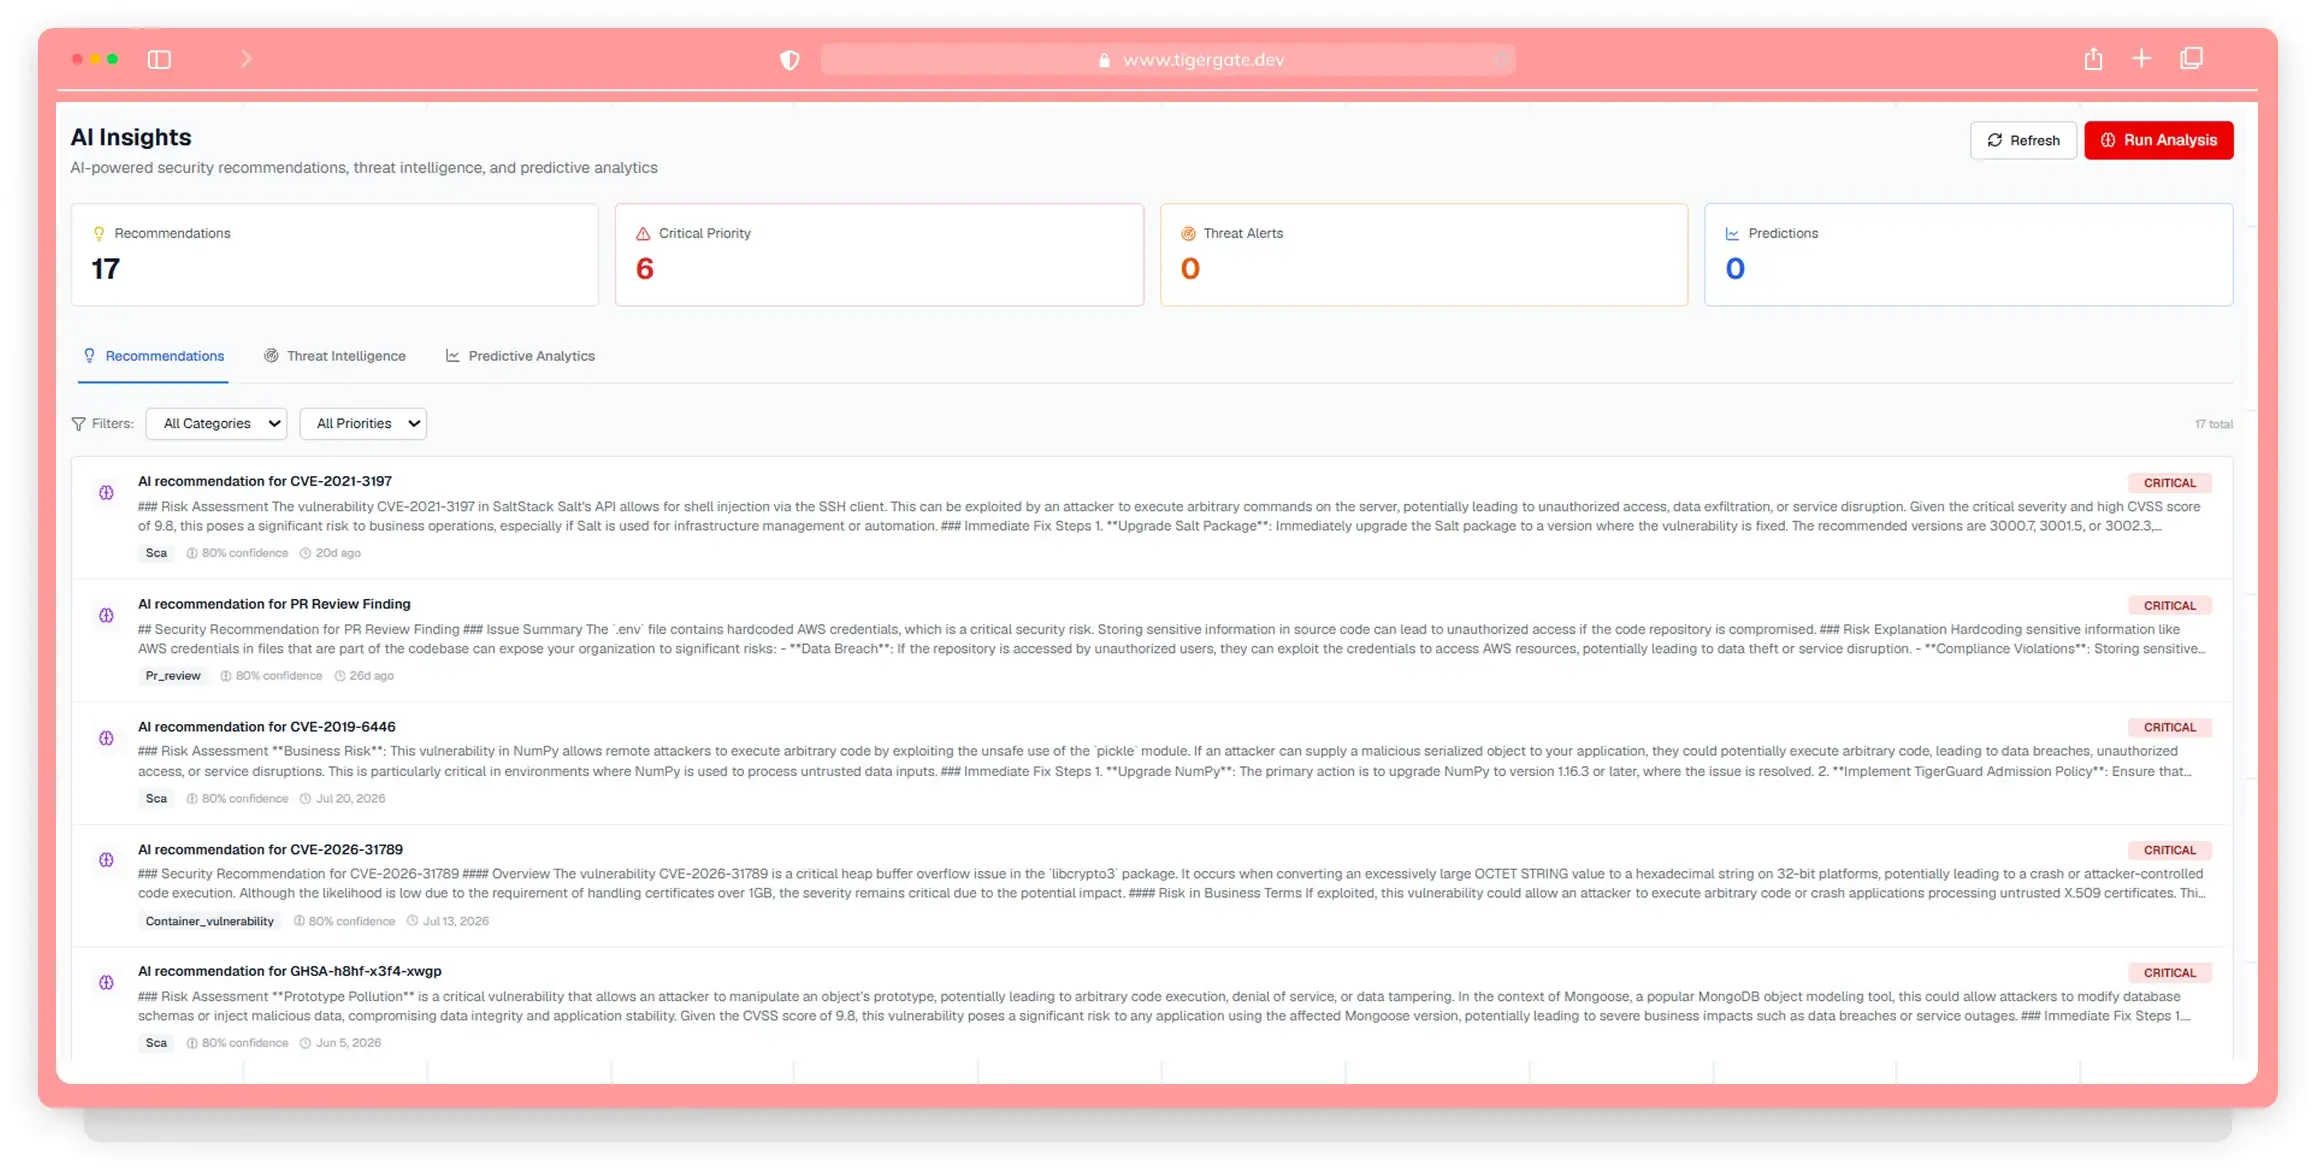
Let AI Find What Matters Most
TigerGate’s AI analyzes vulnerabilities, security findings, and threat data to surface critical risks, prioritize remediation, and provide actionable recommendations. Identify what needs attention first and make faster, smarter security decisions.
Every Product Your Stack Actually Needs
TigerGate is a code-to-cloud security platform: one console for code, cloud, runtime, endpoints, email, servers and AI, with every finding mapped to SOC 2, ISO 27001, PCI DSS and 38+ frameworks. Click any product to see it on tigergate.dev.

Code Security
Find vulnerabilities, secrets and misconfigurations before code ships.
- Static Application Security Testing
- Software Composition Analysis and SBOM
- Code Quality
- Infrastructure as Code Security
- Dynamic Application Security Testing
- API Security

Cloud Security
Posture, identity and data risk across your clouds and Kubernetes clusters.
- Cloud-Native Application Protection
- Cloud Security Posture Management
- Kubernetes Security Posture Management
- Data Security Posture Management
- Cloud Identity Entitlement Management
- Attack Path and Exposure Analysis
- Attack Surface Management

Runtime Protection
eBPF-powered detection and response for the workloads you run.
- eBPF Runtime Protection
- Cloud Workload Protection
- Container Security
- Serverless Security
- Cloud Detection and Response
- Managed Detection and Response

Endpoints, Email and Servers
Protect developer devices, inboxes and Linux servers.
Learn more about Endpoints, Email and Servers
AI Security and Testing
Secure AI and LLM apps, and test your defenses continuously.
Learn more about AI Security and Testing
Compliance
Continuous evidence for 38+ frameworks, ready for your auditor.
Learn more about ComplianceYour next outage is already showing up in your metrics
Let us show you where before your users find out first.
Why Security Teams Choose TigerGate?
TigerGate combines application, cloud, and runtime security in one platform, so your team can find real risk and fix it fast.

Noise Reduction
Correlate static findings with runtime reachability to cut false positives dramatically.

Automated Remediation
Generate pull requests with fix guidance, routed to the right developers automatically.

Kernel-Level Detection
eBPF-powered monitoring that's tamper-proof and can't be bypassed by attackers.
Fast Pipeline Scans
Parallel SAST, SCA, secrets, and IaC scans complete in minutes, never bottlenecking builds.

Multi-Cloud Coverage
Unified visibility across AWS, GCP, Azure, and Oracle Cloud from a single dashboard.

Compliance Automation
Audit-ready evidence for SOC 2, ISO 27001, PCI-DSS, and HIPAA, built into daily delivery.

Rapid Deployment
Connect repositories and deploy the eBPF agent in under 30 minutes flat.
Ecosystem Integrations
Native integrations with Jira, Slack, Splunk, Datadog, and every major CI/CD platform.
Frequently asked questions
All-in-one full stack monitoring
Get a complete view of your application, servers, containers, logs and metrics, and optimize performance with powerful insights.