Secure and comply
 TigerTrust
Enterprise Certificate Management Tool
TigerTrust is the leading PKI management platform that helps enterprises manage PKI, automate certificate lifecycle management, and secure machine identities, from SSL certificate discovery to SSH key lifecycle management.
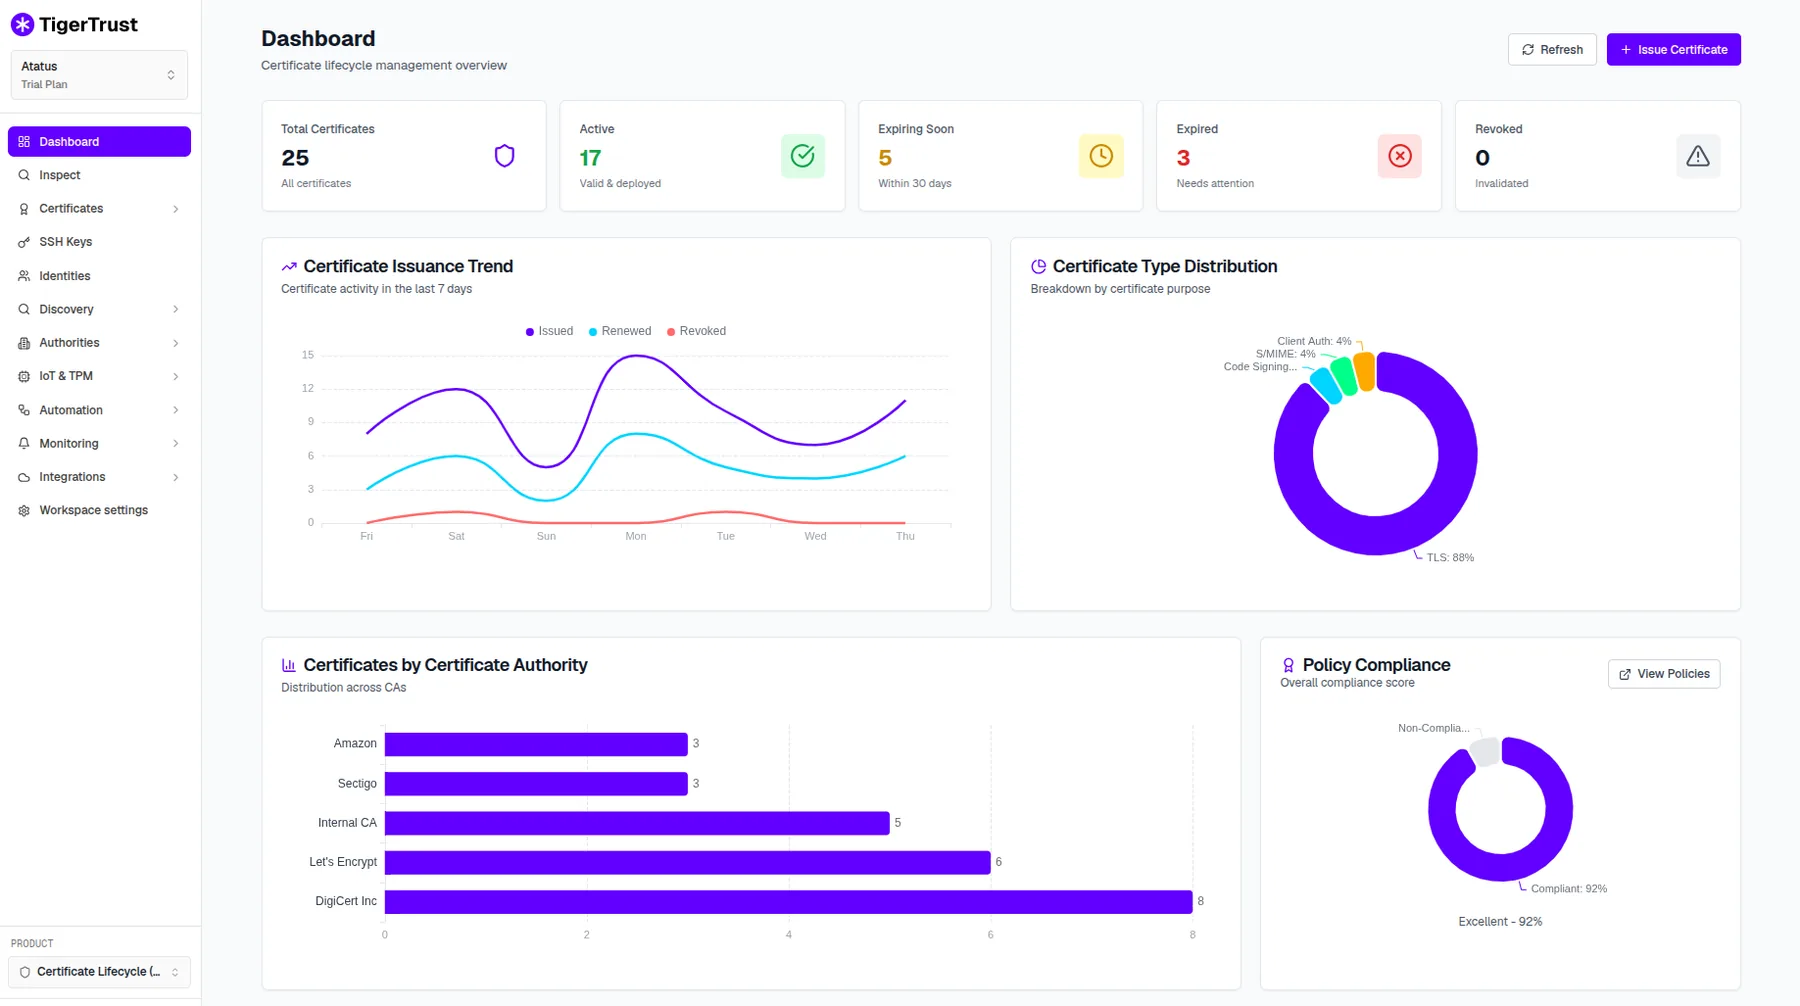
Everything You Need to Tame Certificate Chaos

Automated Certificate Discovery
Scan your entire infrastructure, cloud, on-prem, containers, and IoT, to find every certificate wherever it lives.

Intelligent Lifecycle Automation
Automate renewal well before expiration with multi-CA support and zero-downtime rotation to endpoints.

SSH Key Lifecycle Management
Discover, rotate, and enforce policy on SSH keys across your infrastructure, including orphaned key cleanup.

PKI as a Service
Fully managed public and private certificate authorities with API-first design and multi-tenant workspaces.

Enterprise Code Signing
HSM-protected signing keys with CI/CD pipeline integration across Windows, macOS, and Linux builds.

Enterprise-Grade Security
Policy enforcement, rogue certificate detection, and quantum-safe cryptography support built in.
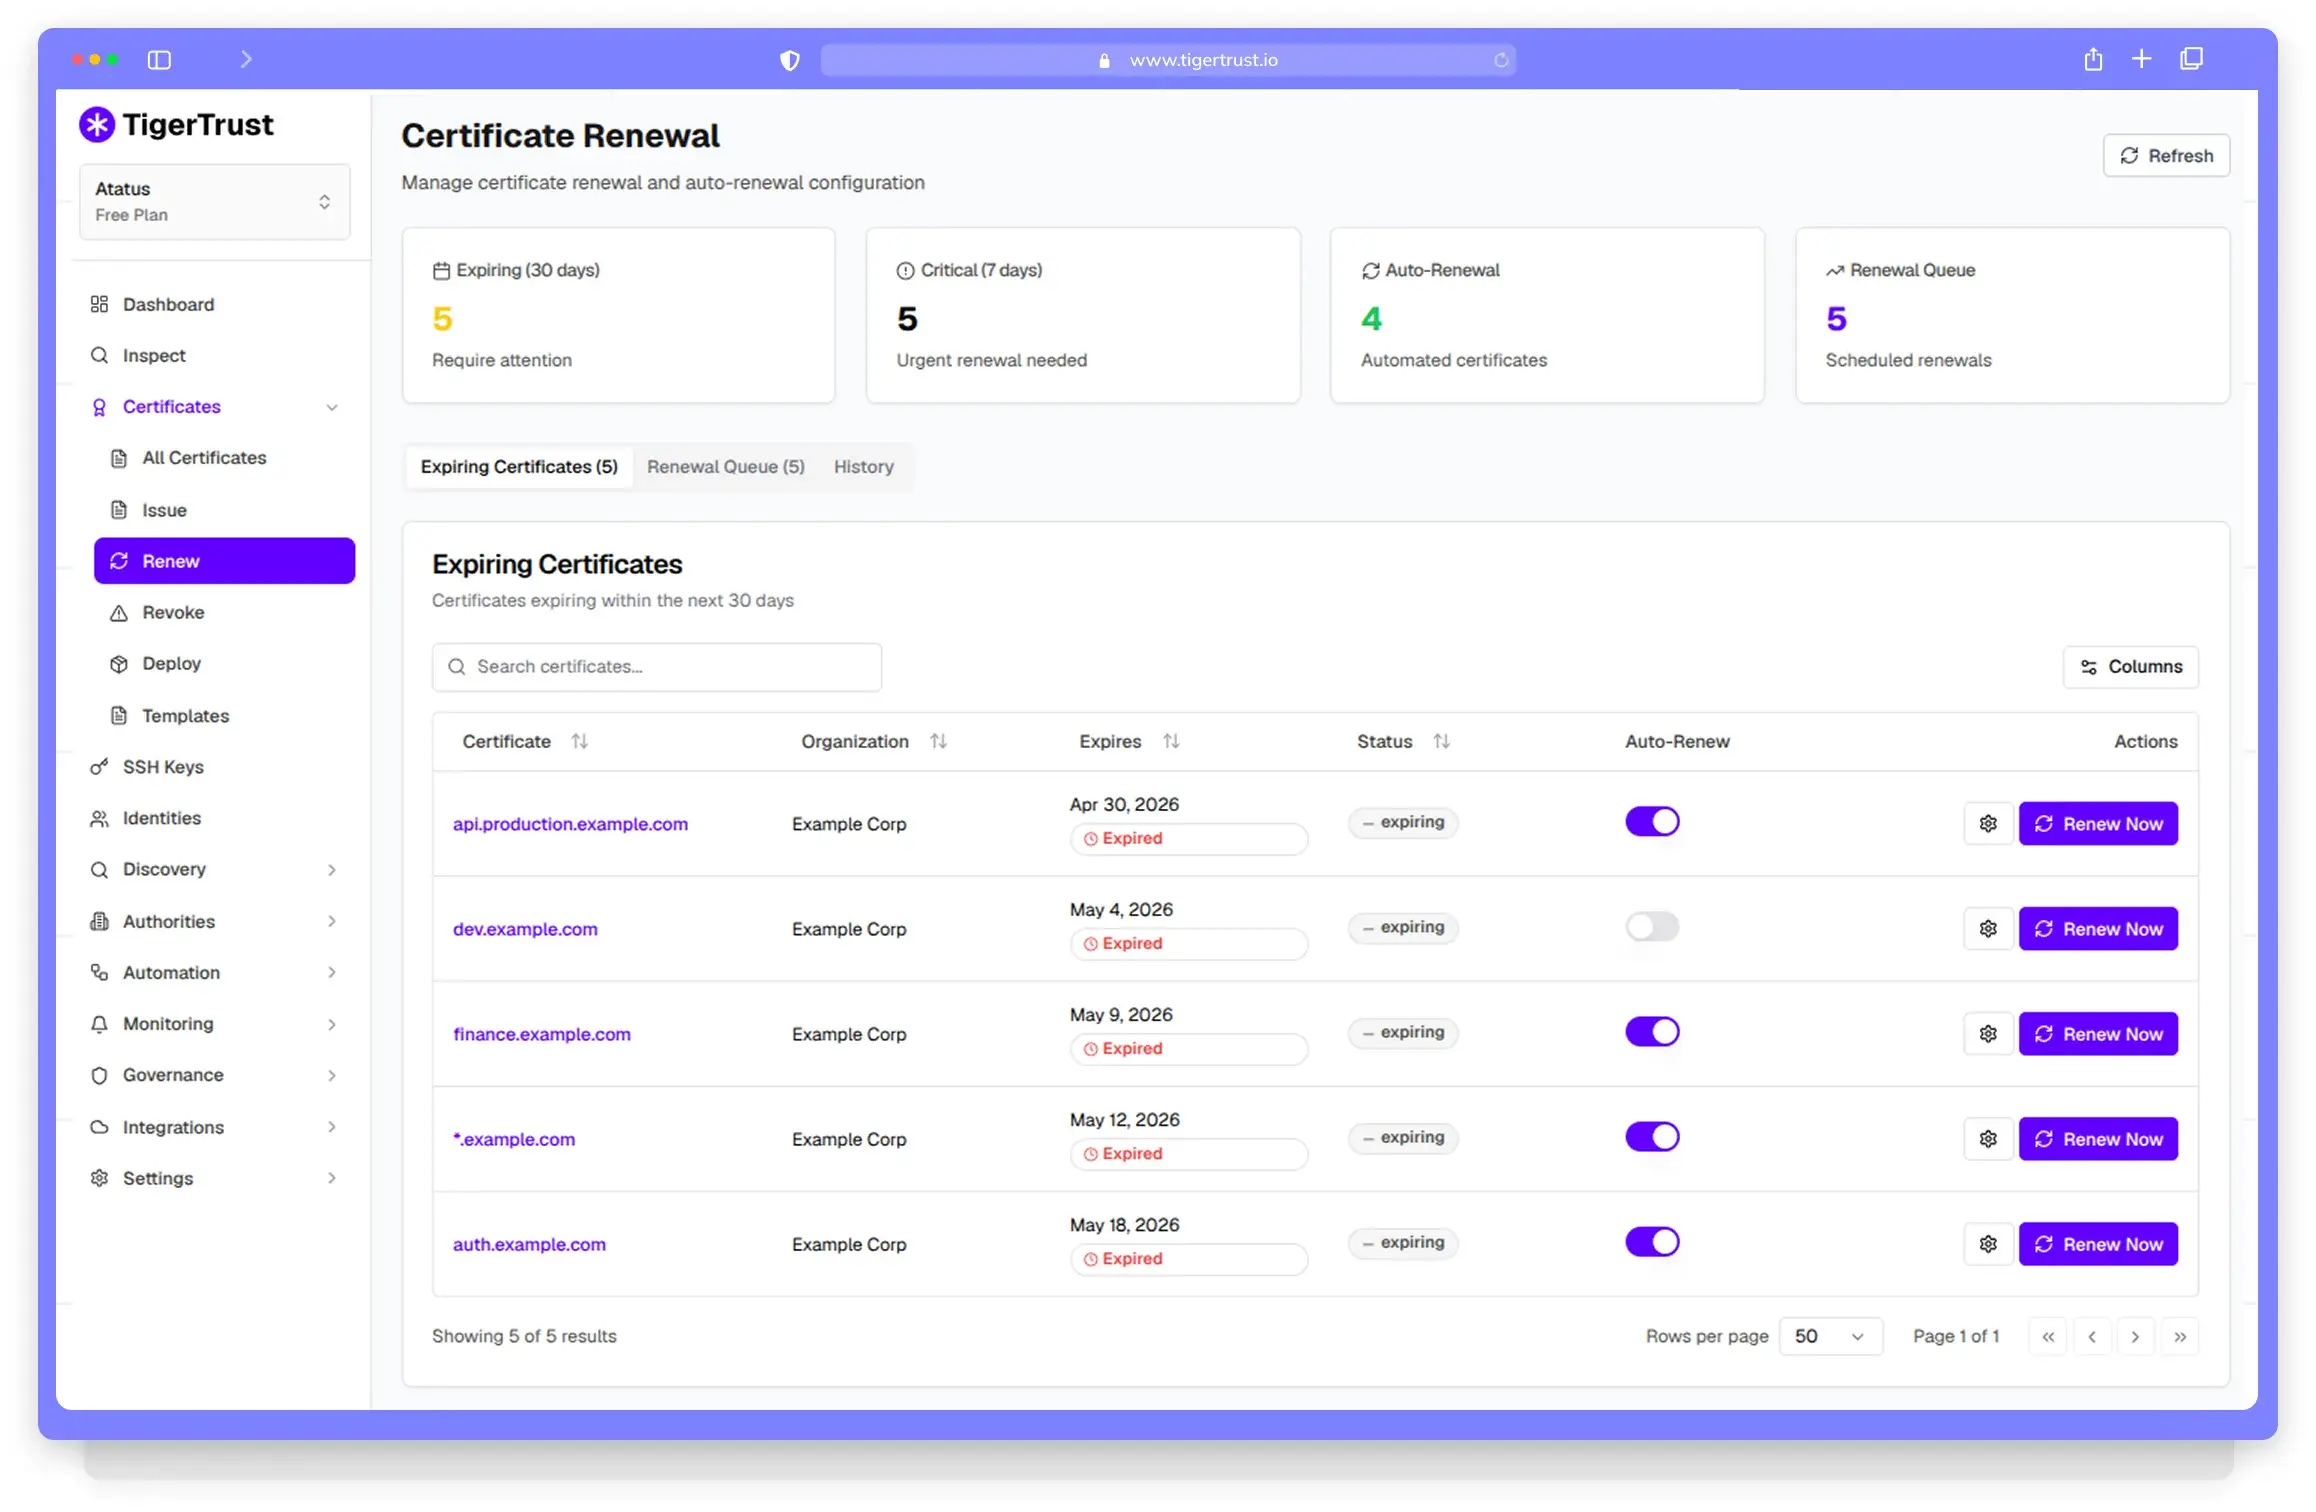
Stop Hunting for Certificates Manually
Certificates can be scattered across networks, AWS, Kubernetes, file systems, and development environments. TigerTrust discovers certificates across your infrastructure and brings them into one centralized view, so your team knows what exists and where.
Try TigerTrust free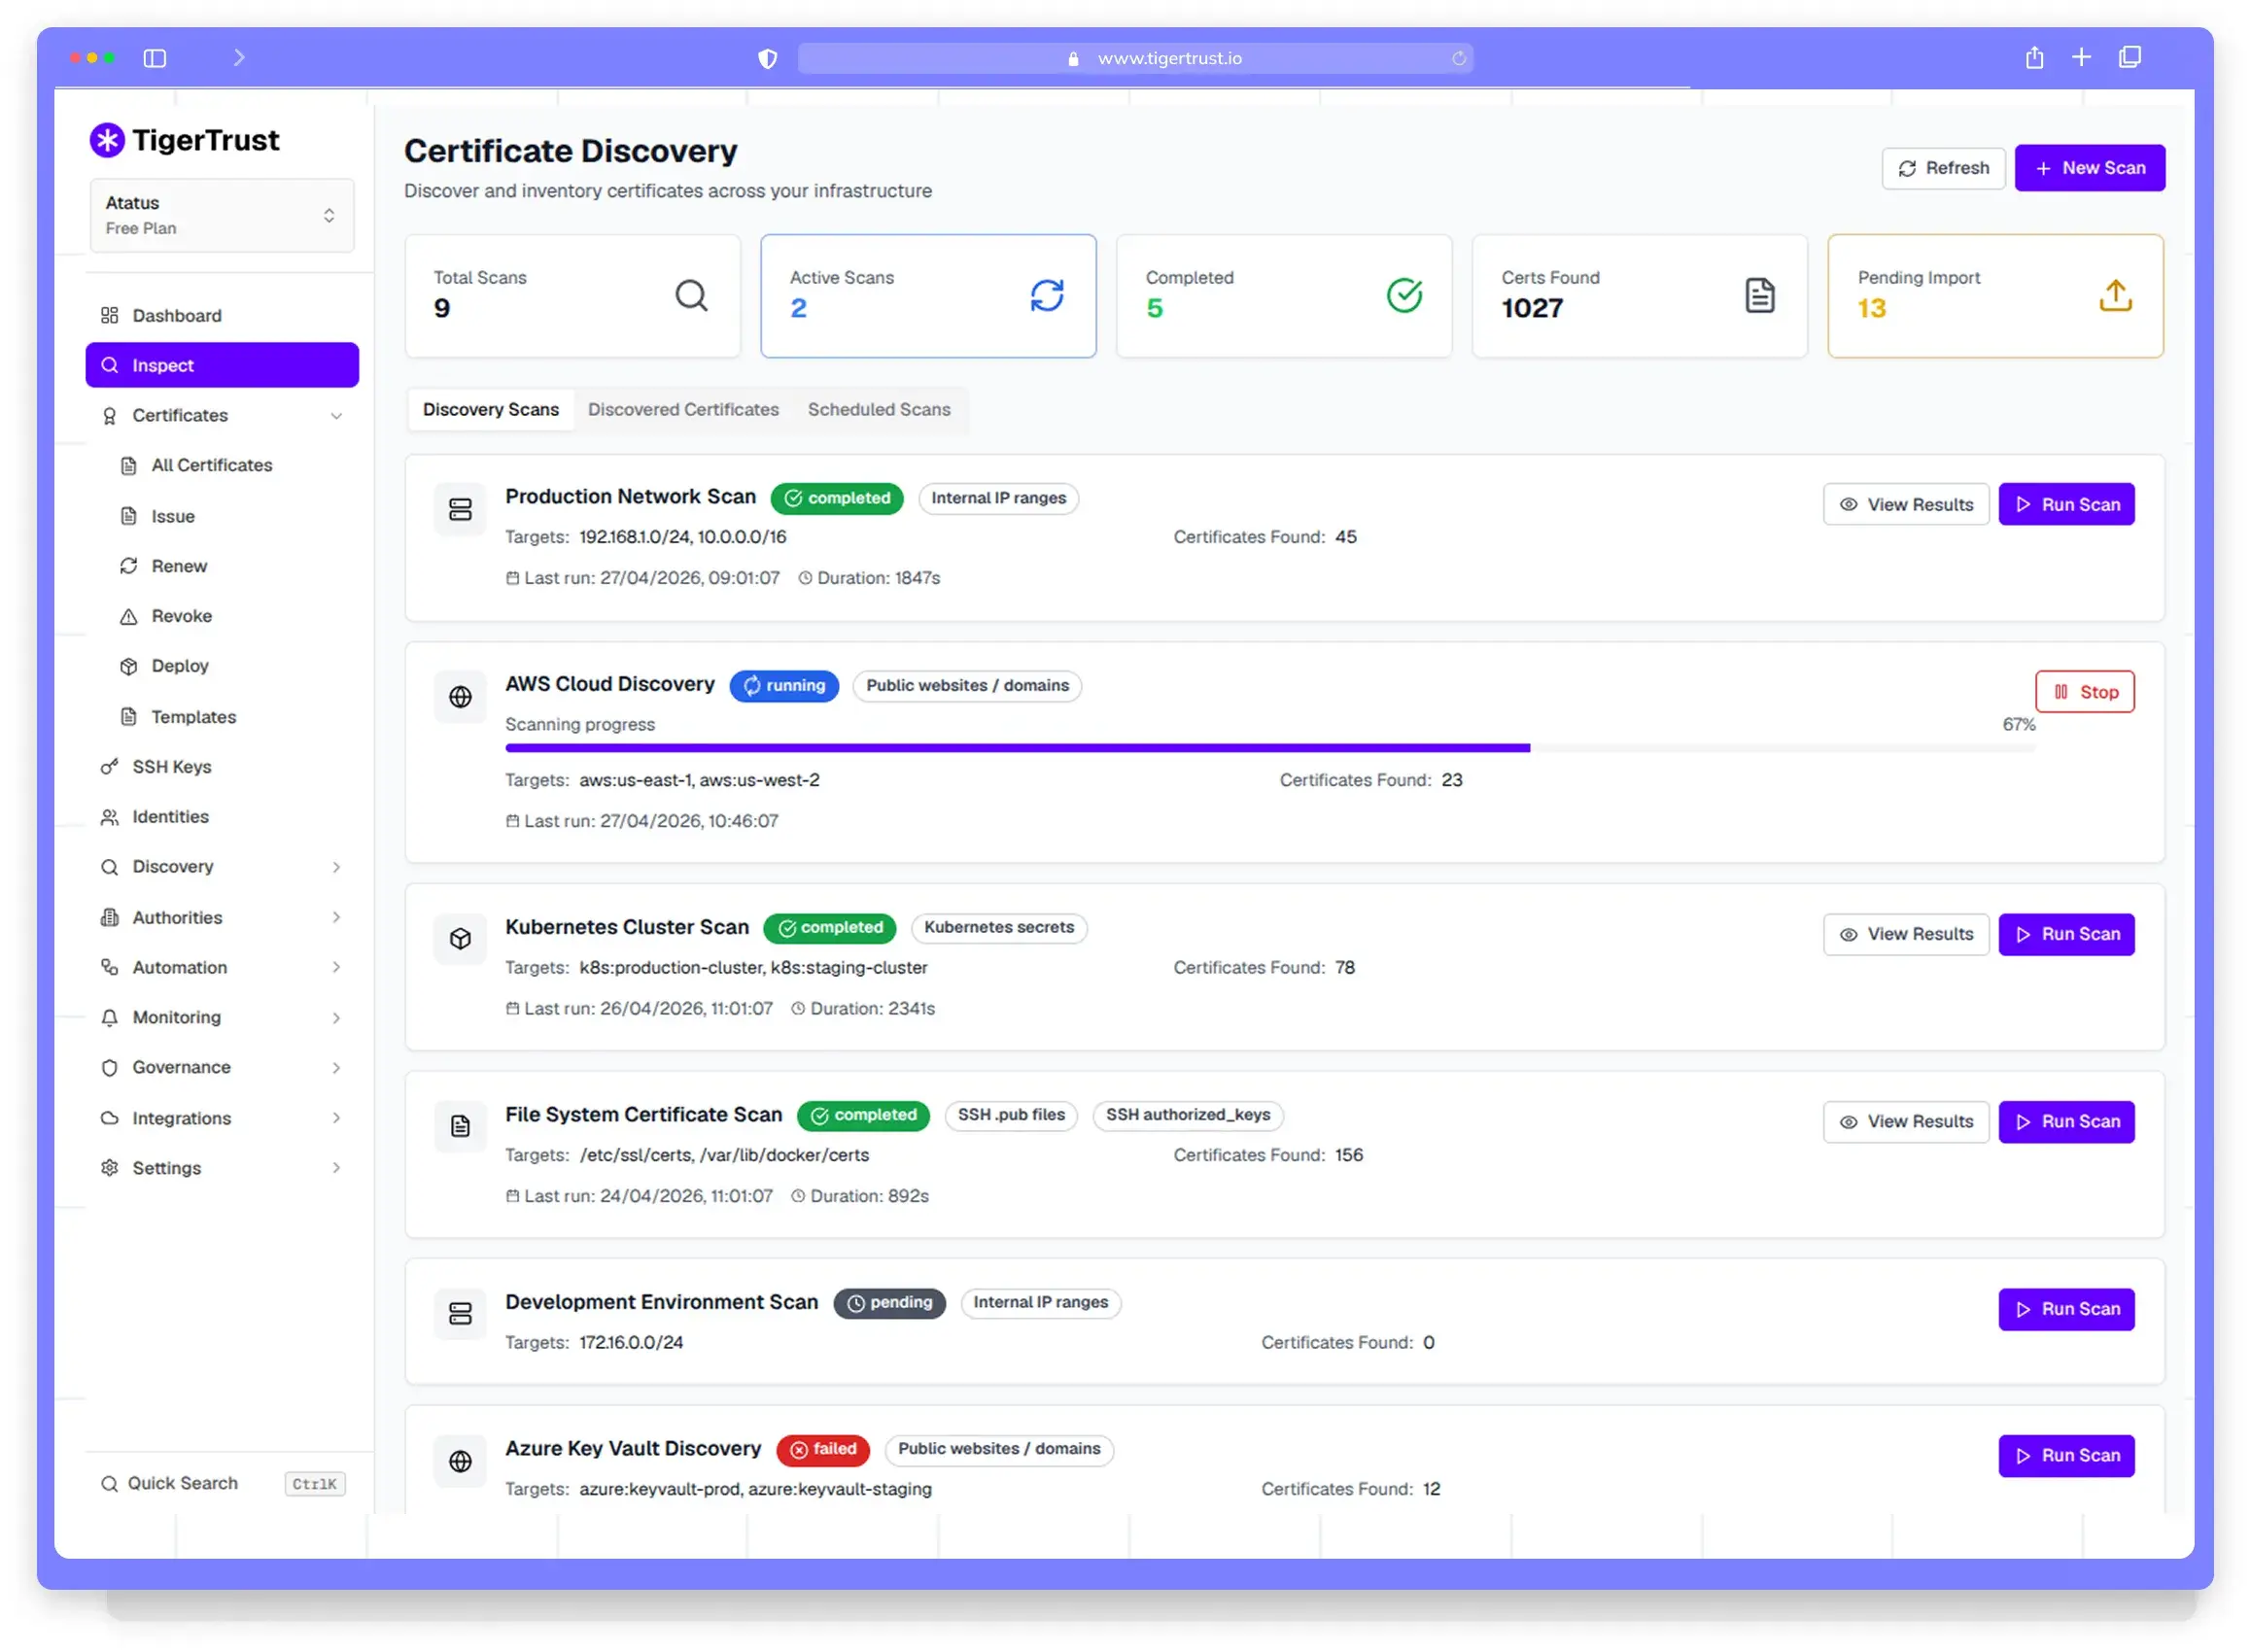
Never Let a Certificate Expire Unexpectedly
An expired certificate can disrupt services and create unnecessary security risks. TigerTrust gives you visibility into certificates nearing expiration and lets you automate renewals, so critical certificates stay ahead of their deadlines.
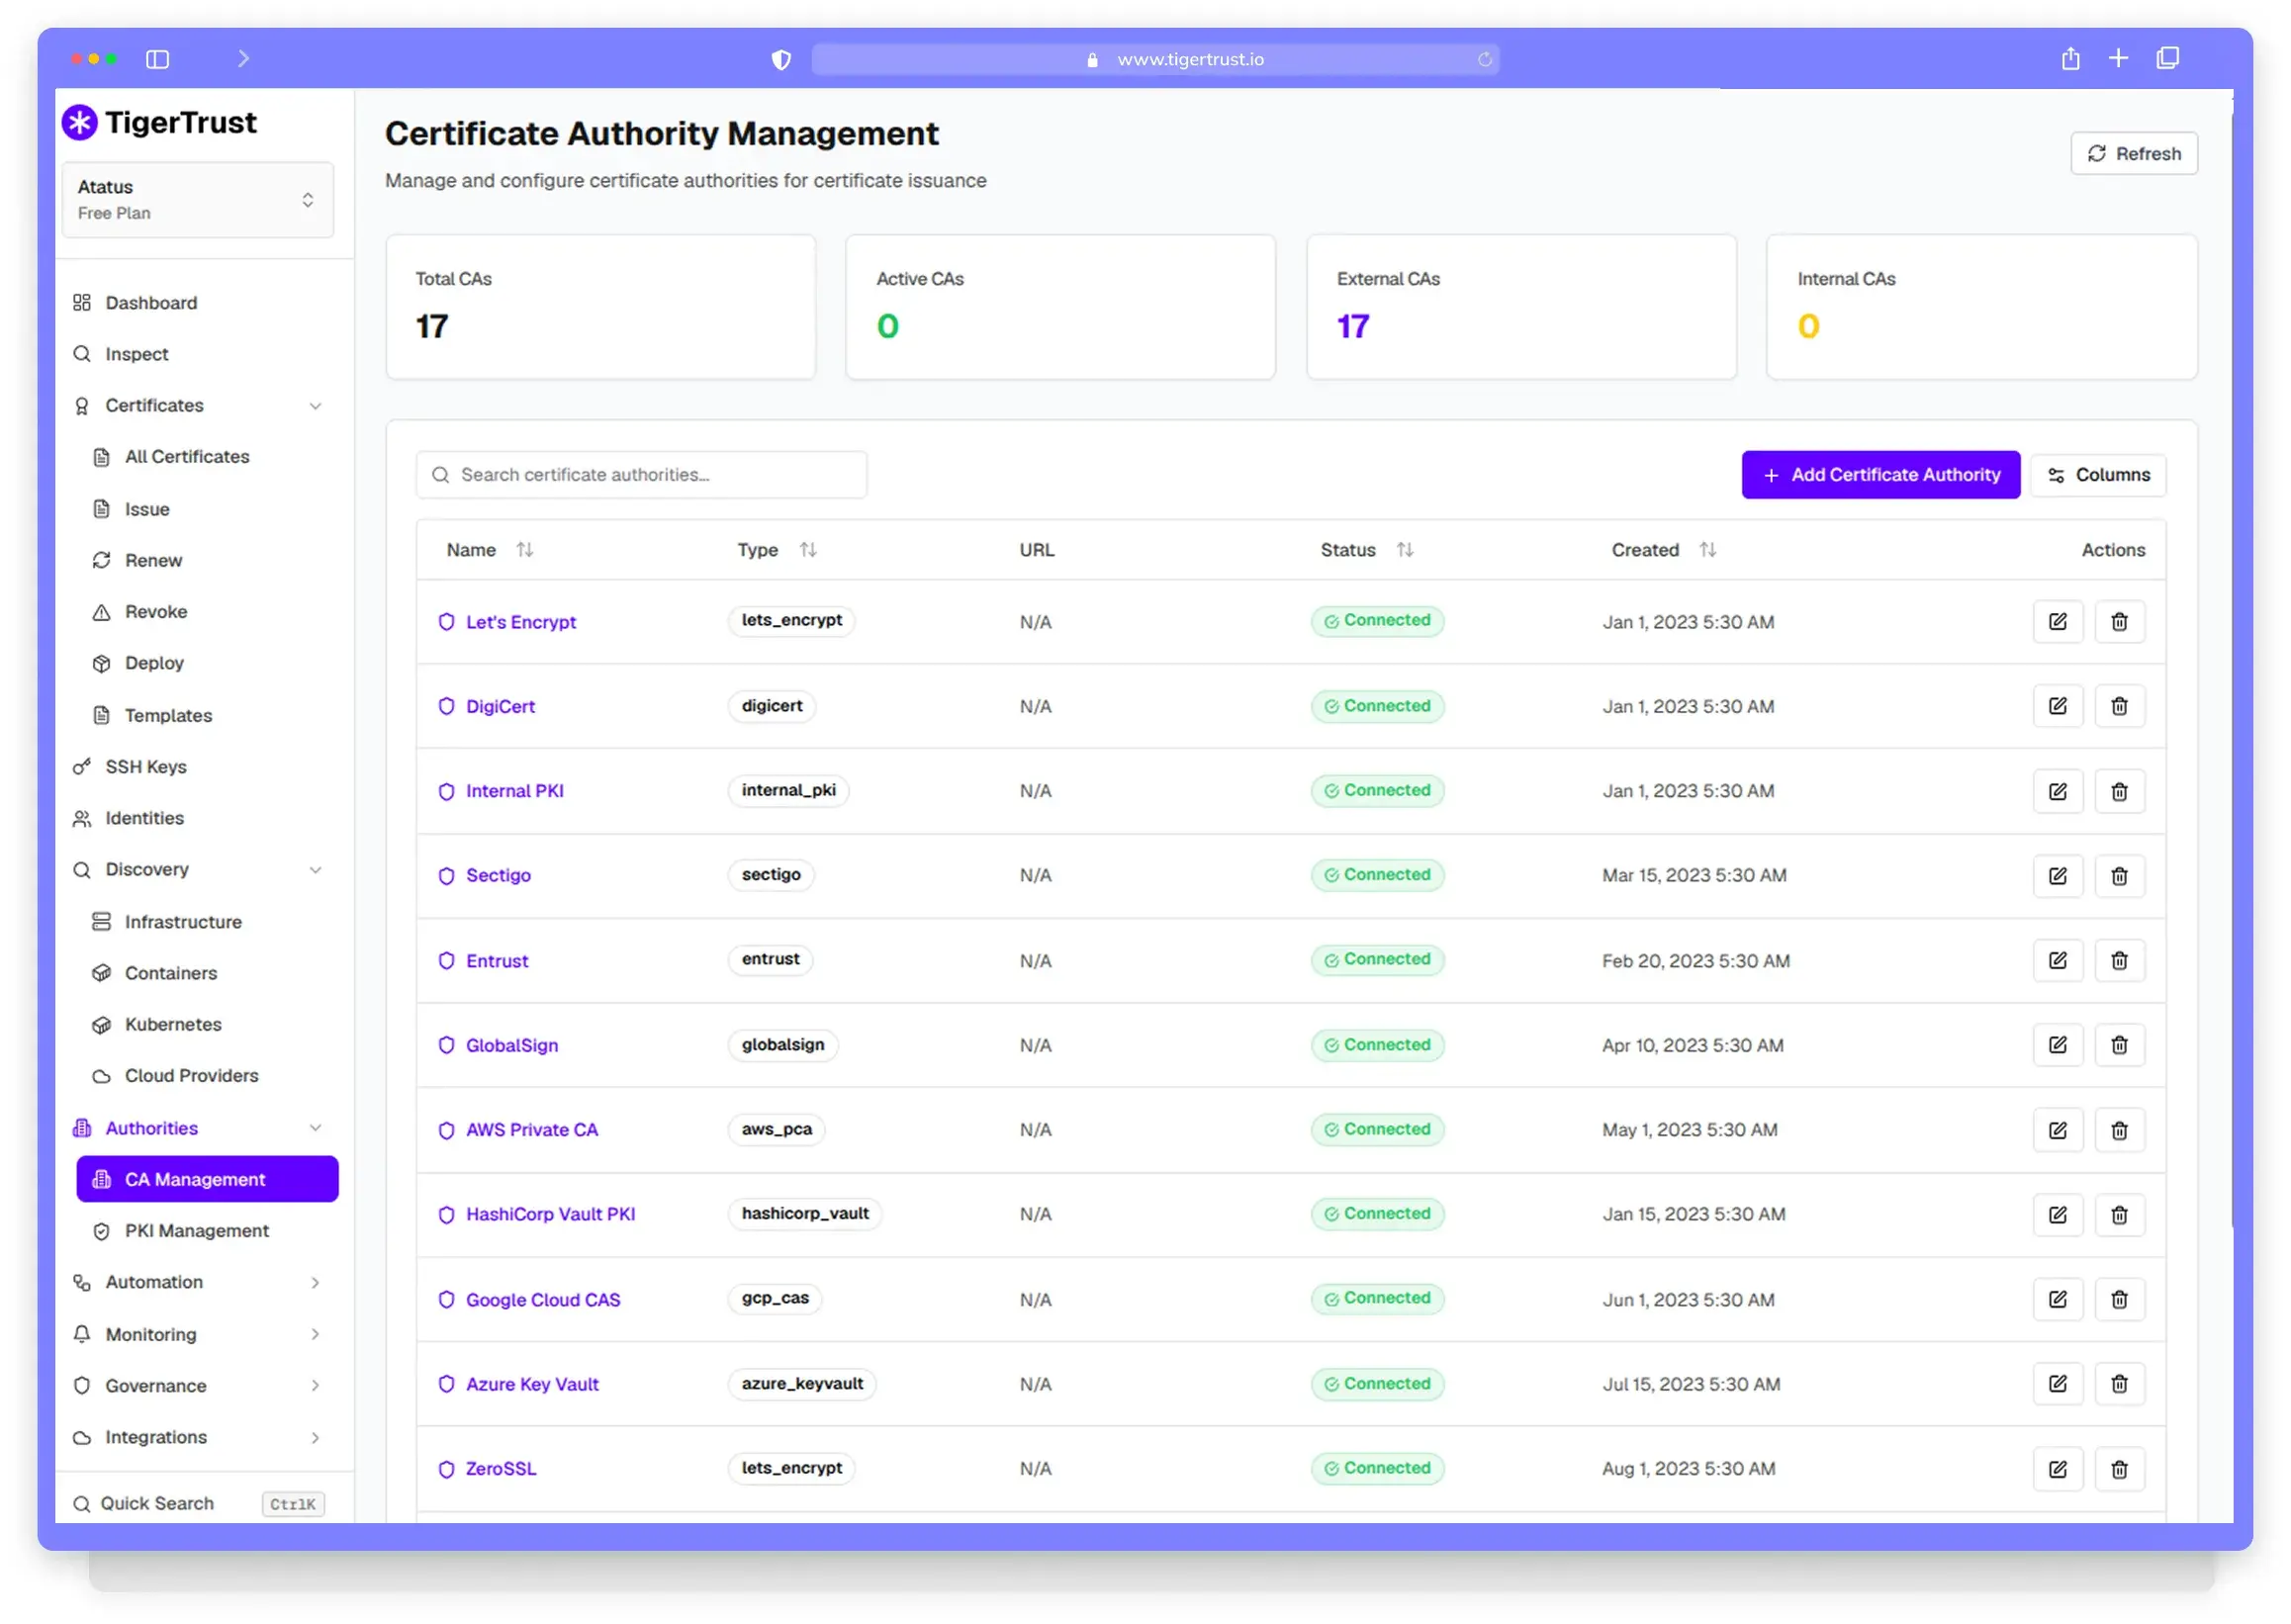
Bring Every Certificate Authority Under Control
Managing certificate authorities across different environments can quickly become complicated. TigerTrust lets you connect and manage your CAs from one place, giving your team centralized control over certificate issuance.
Every Product Your PKI Program Actually Needs
TigerTrust finds every certificate and machine identity you run and automates its lifecycle, so expired certificates never cause an outage. Click any product to see it on tigertrust.io.

Certificate Lifecycle
Find every certificate across cloud, Kubernetes, on-premises and IoT, and renew it before it expires.
- SSL Certificate Discovery
- Certificate Lifecycle Automation
- Kubernetes CLM
- Compliance Monitoring
- AI Analytics

PKI and Machine Identity
Run your own certificate authorities, SSH keys and signing keys, or let TigerTrust manage them.
Learn more about PKI and Machine Identity
Solutions
Certificate automation for the problems and platforms your team deals with.
Learn more about Solutions
Your next outage is already showing up in your metrics
Let us show you where before your users find out first.
Why Enterprises Choose TigerTrust
Real results from day one, not a theoretical roadmap.

Prevent Outages
Proactive monitoring and automated renewal stop certificate-related downtime before it happens.

Save Time
Cut the operational overhead of manual certificate management dramatically.

Ensure Compliance
Comprehensive audit trails and policy enforcement to meet regulatory requirements.
Built for Scale
Manage millions of certificates across cloud, on-prem, and IoT environments.

Reduce Costs
Eliminate emergency firefighting and lower the total cost of certificate ownership.

Strengthen Security
Advanced cryptography and policy controls guard against certificate-based attacks.
Quantum-Ready
Quantum-safe cryptography support keeps you ahead of the next cryptographic shift.
Multi-CA Flexibility
Orchestrate Let's Encrypt, DigiCert, and internal CAs from a single control plane.
Frequently asked questions
All-in-one full stack monitoring
Get a complete view of your application, servers, containers, logs and metrics, and optimize performance with powerful insights.